Jobs and DMs
The AI Recruiter Job Offer Scam, October 2026
Updated 6 October 2026
You get a message from a real-looking recruiter at a company you have heard of, the interview slot is tomorrow, and the calendar invite is already in your inbox. The cost of saying yes is not the hour of your time, it is the W-2, the bank login, or the seed phrase you hand over before you realise the person on the call is not a person at all.
What the AI recruiter scam actually is
It starts the way a real recruiter would reach out. A message on LinkedIn, sometimes a cold email, occasionally a text. The sender has a profile photo, a handful of connections, a job title that sounds right, and a role that pays noticeably more than the market rate for your experience. The hook is a simple combination of flattery and urgency: we found you, we want to move fast, here is a calendar link for tomorrow.
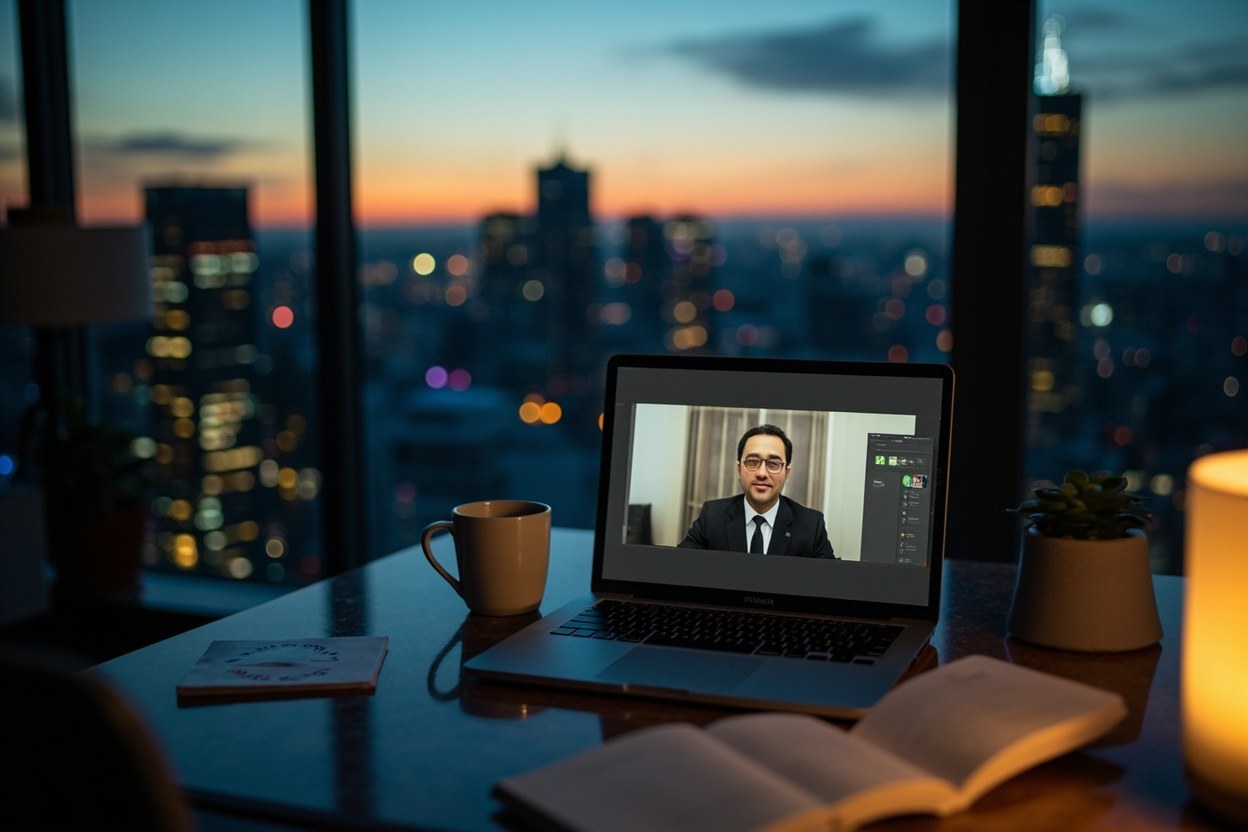
You click the link. A browser tab opens with what looks like a video interview room. The brand is right, the URL is plausible, the layout is polished. A face appears, often a woman in her thirties with a corporate headshot and a headset, and she greets you by name. The questions are credible. The pacing is professional. The whole thing feels like the first round of a real interview process, because it is built out of the real first round of a real interview process, scraped and re-skinned.
The face is not real. The voice is not real. The interviewer is a real-time deepfake, generated from a short video clip of an actual person at the company the scammers are impersonating, or built from a stock avatar and driven by a script the operator types as you answer. The two or three minutes of small talk you do at the start are enough for the system to lift your face, your voice, and your environment. By the time the interview is “wrapping up,” the operator has the raw material to impersonate you on a video call to your bank, or to clone your face onto a selfie you have not taken yet.
The pay-off comes after. You are told you passed, sent an offer letter on real-looking letterhead, and asked to complete onboarding. Onboarding is where the theft happens. Sometimes it is a W-2 and a direct deposit form that gives the operator everything they need to file a fraudulent return in your name. Sometimes it is a screenshot of your ID and a selfie video, which the operator uses to pass a Know Your Customer check on a crypto exchange. Sometimes it is a seed phrase, a one-time code, or a direct transfer to “set up your equipment.” The job never existed, the company may not have heard of you, and by the time the deposit bounces or the W-2 turns up in a tax fraud case, the recruiter’s profile has been deleted and the interview room domain has aged out.
This is not a future problem. Job seekers on Reddit’s r/Scams and on the r/careerguidance subreddit have been posting about deepfake interview rooms since at least 2024, and the FBI’s Internet Crime Complaint Center has a current public service announcement, number I-120424-PSA, dated 6 December 2024, warning that fraudsters are using AI-generated video and voice to pose as recruiters and to spoof interviews. The October 2026 wave is the same pattern wearing a thicker coat of paint, with better avatars, a company name that matches your recent activity, and an interview link that survives a casual glance at the URL bar.
The four shapes the scam takes in October 2026
Scams are easier to recognise when you name the shape, so here are the four versions Malware Zero is seeing right now. They share a backbone: a believable outreach, a too-quick interview, a plausible onboarding step, and a quiet exit. The differences are in what the operator is trying to walk away with.
The first shape is the equipment purchase. You are told the company will ship you a laptop, but first you need to set up the shipping account through a “partner portal,” which turns out to be a crypto payment page or a gift card form. The portal is professional. The portal is fake. The money goes to a wallet that is emptied within minutes. There is no laptop. There is no partner.
The second shape is the W-2 and direct deposit harvest. You are told that, congratulations, you have been hired, and could you complete this onboarding packet. The packet asks for your full legal name, your Social Security number or national insurance number, a scan of your driver’s licence, your bank routing and account number, and a selfie video to verify your identity against the licence. The operator uses this to file a fraudulent tax return in your name, to open new accounts in your name, or to launder money through a payroll account set up in your identity. The real company never sees your details. The offer letter is a PDF made in an afternoon.
The third shape is the crypto job. The role is “remote account manager” or “payment processor,” and the work is receiving transfers into your own crypto exchange account, keeping a percentage, and forwarding the rest. This is not a job. This is money laundering, and you are the mule. The interviews in this shape are sometimes real humans, sometimes deepfakes, and the test transaction that proves “the system works” is real money moved through your account from a compromised source. You become the layer between a theft and a wallet the operator controls, and the only person law enforcement can find is you.
The fourth shape is the seed phrase and one-time code harvest. You are told that to receive your first payment, you need to set up a company wallet, and the “wallet” the operator gives you a link to is a clone of a legitimate wallet site. You enter your existing seed phrase to “restore,” and the clone lifts it. You enter the six-digit code your real wallet app shows you, and the operator uses it to whitelist a new device. Within minutes, your existing balance is moved out, and the wallet you thought was yours is now theirs. This shape is rarer than the others because it requires the target to already hold meaningful crypto, but the targeting has got noticeably better in 2026.
All four shapes share a tell: the interview is too short, the questions are too soft, and there is no friction anywhere. Real interviews have friction. Real recruiters confirm details, push back on gaps, and ask you to repeat things. AI interviewers smile, nod, and let the calendar slot end on time.
How to tell a real recruiter from a deepfake one
The point of the tell is not to make you feel clever. The point is to give you a small handful of checks that take thirty seconds and let you say no without losing face. Run these in order. If any of them fail, you are done with the conversation, and the real recruiter, if they are real, will not be offended.
Check one is the inbound channel. Real recruiters at companies you have applied to email you from the company’s own domain, not a Gmail, not a ProtonMail, not a lookalike such as “acmecorp-hr.com” registered last week. Real recruiters at companies you have not applied to will use a LinkedIn profile with a long work history, mutual connections, and a recruiter title that matches an open role on the company’s actual careers page. If the message arrived in your LinkedIn DMs and the profile was created in the last ninety days, with a stock photo and a single job listed, treat it as hostile until proven otherwise.
Check two is the calendar link. Real recruiters send you a Calendly, a Google appointment schedule, or a Microsoft Bookings link tied to a company email. The link you receive will be from a domain the company owns. The link you receive in a scam is often from a “video interview platform” you have never heard of, hosted on a domain that was registered recently, with a TLS certificate that is only a few days old. You can see the registration age of any domain at whois.com or by using a lookup at securitytrails.com. If the interview platform domain is less than a year old and the company the recruiter claims to work for has been around for decades, that is your answer.
Check three is the company careers page. Open a new tab. Do not click any link in the message. Type the company name into your browser yourself. Find their careers page. Search for the job title the recruiter mentioned. If the role is not listed, the recruiter is not recruiting. Real recruiters post roles on the company’s own ATS before they start cold-messaging candidates, because that is how their hiring managers measure them. If the role is listed, look at the application process. Real processes do not start with a same-day video interview from a stranger.
Check four is the interview itself, if you have somehow got that far. Real interviewers have backgrounds that look like offices, or the corporate virtual background the company actually uses, with logos in the right places. Deepfake avatars often have backgrounds that are slightly wrong, a bookshelf that bends, a window that does not match the light direction, a blur around the edges of the head that does not match the rest of the frame. The lip sync is usually a frame or two off. The eyes do not quite track the camera. The blink rate is too low, because the underlying video is a still. If anything feels off, freeze the call, take a screenshot, and end it. You can always restart a real interview. You cannot undo handing over your W-2.
Check five is the onboarding ask. The single most reliable tell is the first thing the onboarding form asks for. If the answer is your Social Security number, your national insurance number, your bank login, a one-time code, a seed phrase, a selfie video, or a payment of any kind, you are not being hired. You are being robbed. Real onboarding happens after a contract is signed, through the company’s own HR portal, with paperwork you can verify by calling the company’s switchboard. Anyone who asks for any of the above in the first twenty-four hours of a “job” is not your employer.
What to do if you have already clicked the interview link
Damage control is the same as it is for any credential theft, with a few additions that matter here. Move fast. The window between the interview ending and the operator using what they lifted is often less than an hour, because the operator is sitting in a chat panel on the other side of the call and is acting on the information in real time.
First, if you entered a seed phrase, treat every wallet that ever used that seed as compromised. Move funds to a brand new wallet generated on a device that has never seen the old one. Do not “just change the password.” A seed phrase is the keys, not the password. There is no rotation that fixes a leaked seed.
Second, if you submitted a W-2 form or a scan of your ID, assume the worst. In the United States, file an IRS Identity Theft Affidavit, Form 14039, and request an Identity Protection PIN at irs.gov/ippin. In the United Kingdom, contact Action Fraud at actionfraud.police.uk and consider a Cifas Protective Registration, which puts a marker on your file so lenders do extra checks. In Australia, contact IDCARE on 1800 595 160 and consider applying for a Commonwealth Victims’ Certificate. The same logic applies in most countries: tell the tax authority first, then the credit bureau, then the banks.
Third, if you sent money, the recovery picture is grim but not zero. Crypto payments are usually gone, but report the transaction to the exchange you sent from and to the exchange that received it. Gift card payments can sometimes be stopped if you call the retailer within minutes. Bank transfers can be recalled by your bank if the receiving account is still flagged as a scam account, which is a coin flip. Do not pay anyone who contacts you offering to recover the money for a fee. That is the recovery scam, and it is run by the same operators.
Fourth, if you did a video interview, assume your face and voice have been lifted. Any service that uses your face or voice for biometric login should be re-enrolled from scratch, using a fresh enrolment, and you should turn on every available form of second factor. Banks, in particular, should be told that your face and voice may be in someone else’s training set.
Fifth, report the profile. LinkedIn has a “Report this profile” link on every profile page, and the relevant category is “Fake account or impersonation.” Report the interview platform to the abuse address at their registrar, which you can find at whois.com. In the United States, file a complaint with the FBI’s Internet Crime Complaint Center at ic3.gov and include the URL of the interview room, the username of the recruiter, and any wallet addresses you sent to. In the United Kingdom, report to Action Fraud. In Australia, report to Scamwatch. The reports feed the same databases the banks and the telecoms use to flag accounts, and the more reports a wallet or a domain has, the faster it gets burned.
The law and the recovery, briefly
One final thing. The scammers are running this as a volume business, and they A/B test what works. If you got a message this week, the version you saw is the version that has been converting in your city, in your industry, in your age bracket. That is a cold comfort, but it is the truth, and the truth is what you need to push back. The next recruiter who messages you is, statistically, more likely to be running this scam than they were a year ago, and the only thing that protects you is the habit of running the five checks before you click anything.
Quick answers
- Can a deepfake interview really look that real?
- Yes. The current generation of real-time deepfake video can hold a face-to-face conversation, respond to a script, and survive a thirty-minute call without breaking, which is longer than most first-round interviews run. The tells are subtle, which is why the domain and the careers page checks matter more than trying to spot the avatar on the call.
- Is the company I got the offer from actually involved?
- Almost always no. The company’s name and branding are stolen. The HR person you think you spoke to is an AI avatar. The careers page is the only place that tells the truth, so always check the open role there before you do anything else.
- I already sent my W-2 details. What now?
- Treat your identity as compromised. In the US, file IRS Form 14039 and request an Identity Protection PIN. In the UK, contact Action Fraud and consider Cifas Protective Registration. In Australia, contact IDCARE and consider a Commonwealth Victims’ Certificate. Then notify your bank, freeze your credit files, and keep a written log of every step.
- I sent crypto to a wallet the “recruiter” gave me. Can I get it back?
- Honest answer: usually no. Crypto transactions are final, and the receiving wallet is typically emptied within minutes. Your best move is to report the receiving wallet to the exchange that holds it, file a complaint with IC3, Action Fraud, or Scamwatch, and do not pay anyone who contacts you offering to recover the money for a fee.
This is general safety information, not legal advice. Scams change. If you need an official desk: FTC ReportFraud or IC3.